How to use Citrix SecurAccess from your Android device
Install Citrix SecurAccess from your Play Store. First-time users must create a connection to NetScaler Gateway by adding the server in the non-MDM case. For subsequent uses, you can connect to an existing connection or add a connection, and edit existing connections as well, if allowed by your administrator in an MDM deployment. You can also view the logs and take appropriate actions accordingly.
Notes:
-
Connections deployed through MDM cannot be edited.
-
You might be prompted to grant the Query all packages consent to the Citrix SecurAccess app. Once the consent is granted, the Citrix SecurAccess app:
-
Receives the package install notification from the operating system.
-
Restarts the Always On VPN.
When you connect to your VPN profile for the first time, you are prompted to provide consent (required by Google policies) to collect information about the installed package. If you grant the consent, the VPN connection is initiated. If you deny the consent, the VPN connection is aborted. The consent screen does not reappear once the consent has been granted. -
Add a connection
Note: This step is required only in a non-MDM case.
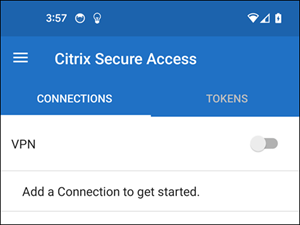
After you install Citrix SecurAccess and open the app on your Android device, the following screen appears.
-
Click + to add a connection.
-
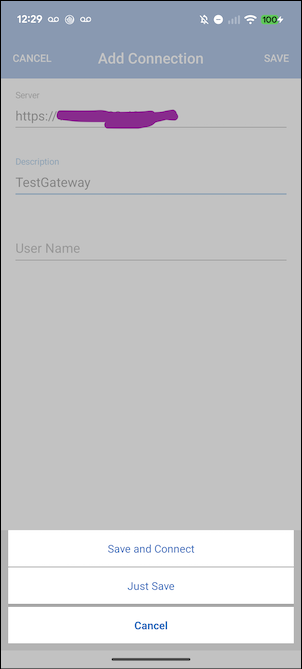
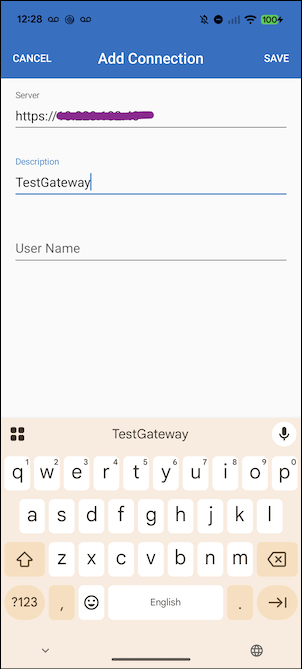
Enter the base URL (for example, My company) and the name for the VPN connection. Optionally, you can enter the user name.
-
Click Save and then click Save and Connect or Just Save as appropriate.
-
Provide authentication credentials for your server and tap LOG IN or Done on the keypad.
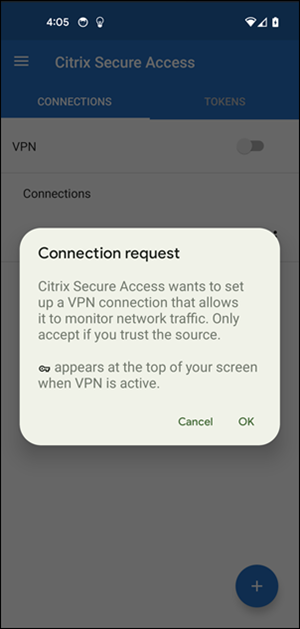
The connection request message appears. Click OK.
Note: This message appears only the first time that any VPN connection is established by Citrix SecurAccess. If the user allows the connection for the first time, this message is not shown again until the user uninstalls and reinstalls the app.
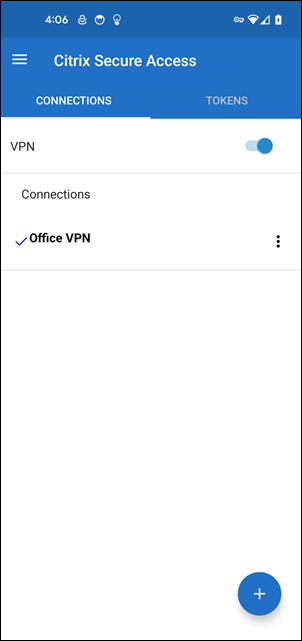
Note: To log out from Citrix SecurAccess, turn the VPN switch OFF.
Modify or delete an existing connection
You can edit or delete a connection after you log out from Citrix SecurAccess.
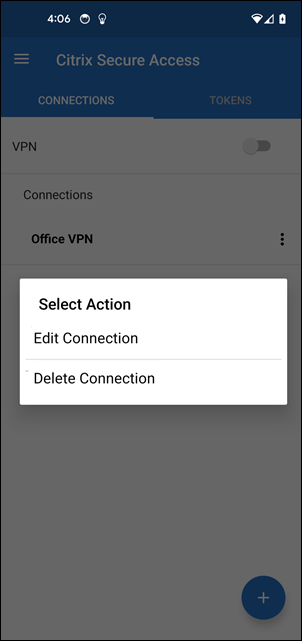
Tap and hold the server name and select Edit Connection or Delete Connection.
Reconnect to NetScaler Gateway after a VPN connection failure
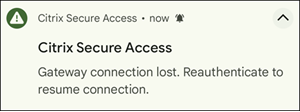
The Citrix SecurAccess client for Android prompts you to reauthenticate with NetScaler Gateway when a VPN connection is lost. You are notified on the UI and the notification panel of your Android device indicating that the connection to NetScaler Gateway is lost and that you must reauthenticate to resume the connection.
Allow local network access permission on Android 17 and later
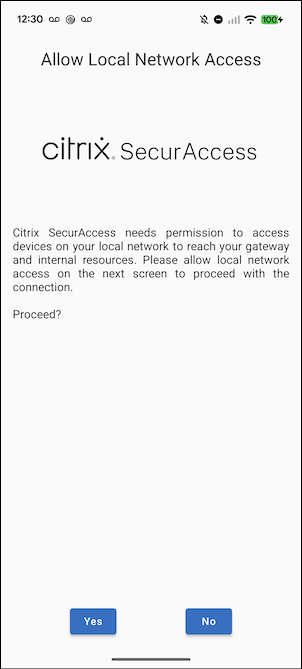
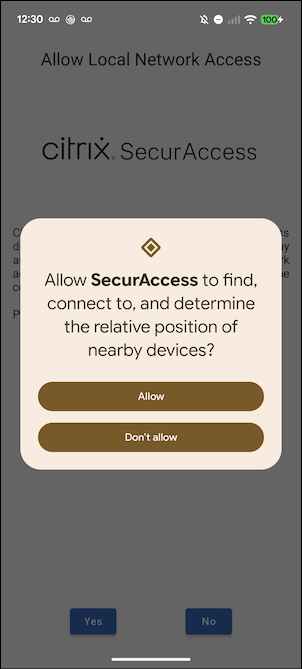
Starting from Citrix SecurAccess for Android release 26.08.1, users who install, reinstall, or update the application on Android 17 and later, they are prompted to allow local network access. If access is denied, certain local network services, such as Wi-Fi printers, might be unavailable when a VPN session begins.
MDM administrators are advised to pre‑grant this permission to the Citrix SecurAccess application.
Receive or block notifications on Android 13 and later
Starting from Citrix SecurAccess for Android release 23.12.1, users who install, reinstall, or update the application on Android 13 and later, they are prompted to allow notifications. If notifications are denied, users do not receive VPN status or push notifications from Citrix SecurAccess.
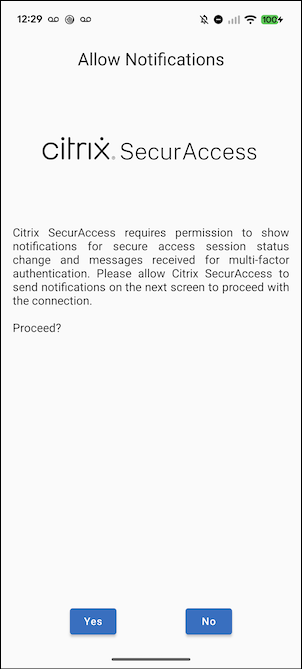
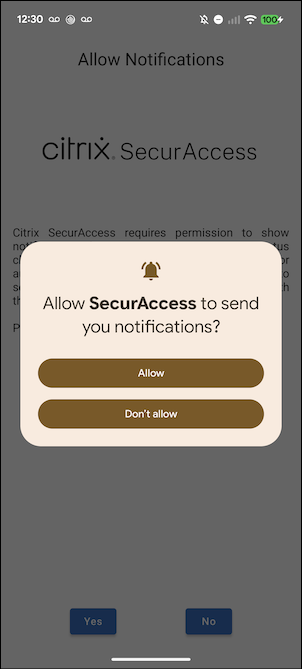
You can navigate to Settings > Notifications on your Android device to change the notification permissions.
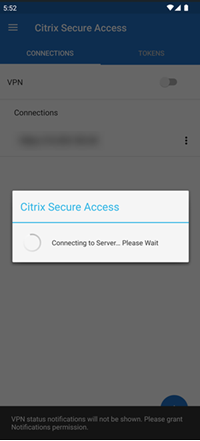
In the following example, the VPN status notifications have been disabled.
Block untrusted servers
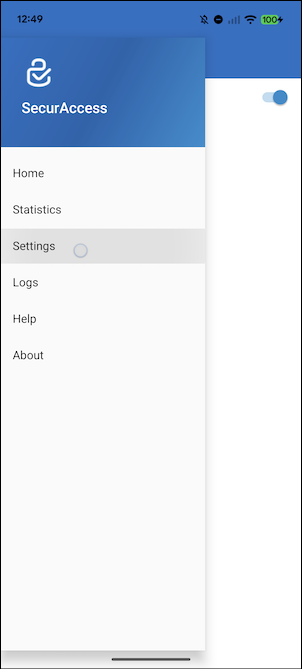
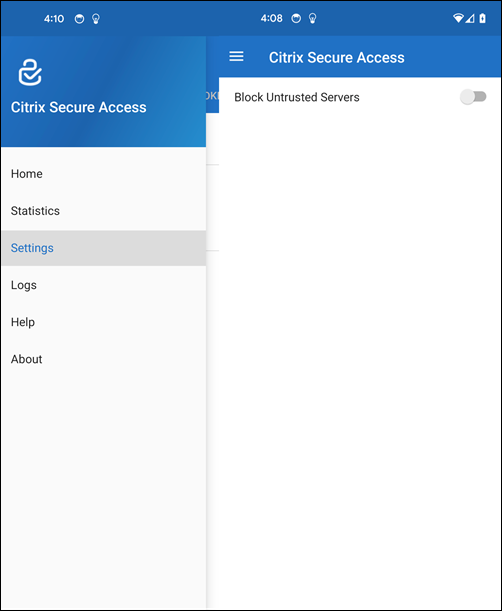
Citrix SecurAccess does not connect to untrusted servers, by default. Untrusted servers refer to servers using self-signed certificates or not having a trusted root certificate for the gateway. To allow these types of connections, you can turn Block Untrusted Servers switch OFF.
Enable debug logs
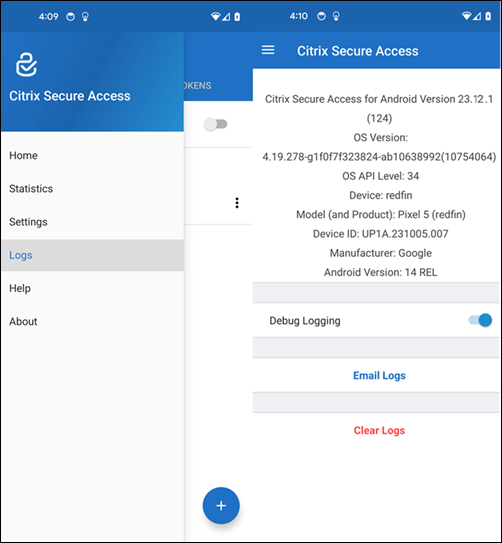
Capturing debug logs is a critical part of troubleshooting or reporting issues to Citrix Support. Tap the Debug Logging switch ON to turn on debug logging for Citrix SecurAccess. You can email the logs when troubleshooting connection issues using the Email Logs link.
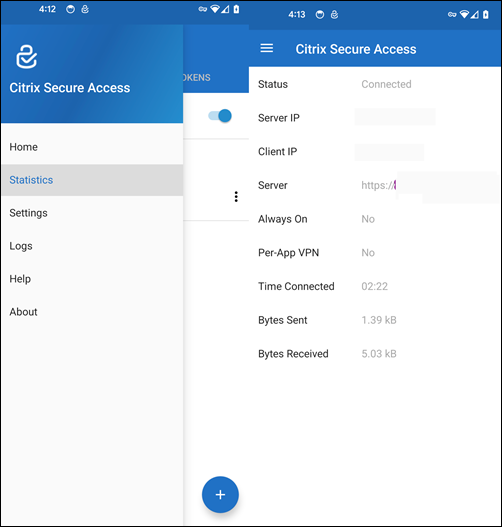
View statistics
You can view the connection statistics when the VPN is connected.
Password tokens
You can add a 6-digit password token as a second factor authentication. This code uses the time-based one time password protocol to generate the OTP code.
You can add a password token manually or register a password token using the QR code scan method. Second factor authentication using push notifications is not enabled if you choose to enter the token manually.
Register a password token
-
Log in to your organization's manage one-time PIN page in your web browser on a desktop or a laptop.
-
Click Add Device.
-
Enter a name for your device, then click Go.A QR code is generated.
Add a password token by scanning the QR code on the browser
-
Navigate to Tokens tab on the Home view.
-
Tap + and tap Scan QR Code.
-
Focus the camera on the QR code on your browser.
Citrix SecurAccess auto-populates the device name and secret key.
Alternatively, you can manually enter the secret key that appears above the QR code.
Citrix SecurAccess validates the QR code and then registers with the gateway for push notifications. If there are no errors in the registration process, the token is successfully added to the tokens tab.
Note:
-
You must allow camera permissions for Citrix SecurAccess to capture the QR code.
-
You must enable the device PIN/password on your device.
Add a password token manually
-
Navigate to Tokens tab on the Home view.
-
Tap + and tap Enter Manually.
-
Enter the device name and the secret key as it appears on the password token generated on the browser.
Help topics
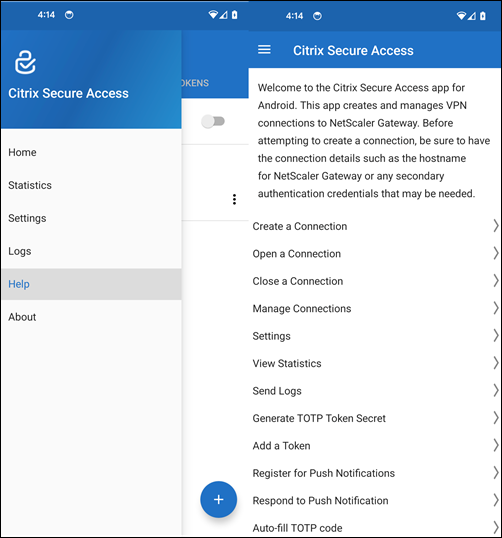
For more information about how to use Citrix SecurAccess, see Help.